Home / Security audit
Cyber & data security auditFind the gaps before attackers do
Our audit team assesses your IT infrastructure, websites, applications and data handling against recognised standards — ISO/IEC 27001, OWASP, CERT-In guidelines and the DPDP Act 2023 — and gives you a clear, prioritised plan to fix what matters.
National Cyber Security Research CouncilManoj Kumar Jain · ID NCSRCASSOC1017910
Cyber security audit
- VAPT: internal and external
- Network architecture, segmentation and firewall rules
- Server and endpoint hardening
- Active Directory and password policy
- Patch, antivirus and EDR review
- Wi-Fi and wireless security
- Email security and phishing simulation
- Cloud configuration review
- Backup, DR and ransomware readiness
Website security (ethical hacking)
- OWASP Top 10 testing
- SQL and command injection
- XSS and CSRF
- Authentication, session and access control (IDOR)
- SSL/TLS and security headers
- API security (REST / SOAP)
- Mobile app security (Android / iOS)
- CMS plugin vulnerabilities, malware and defacement
- Secure code review (SAST)
Data security audit
- Data discovery and classification
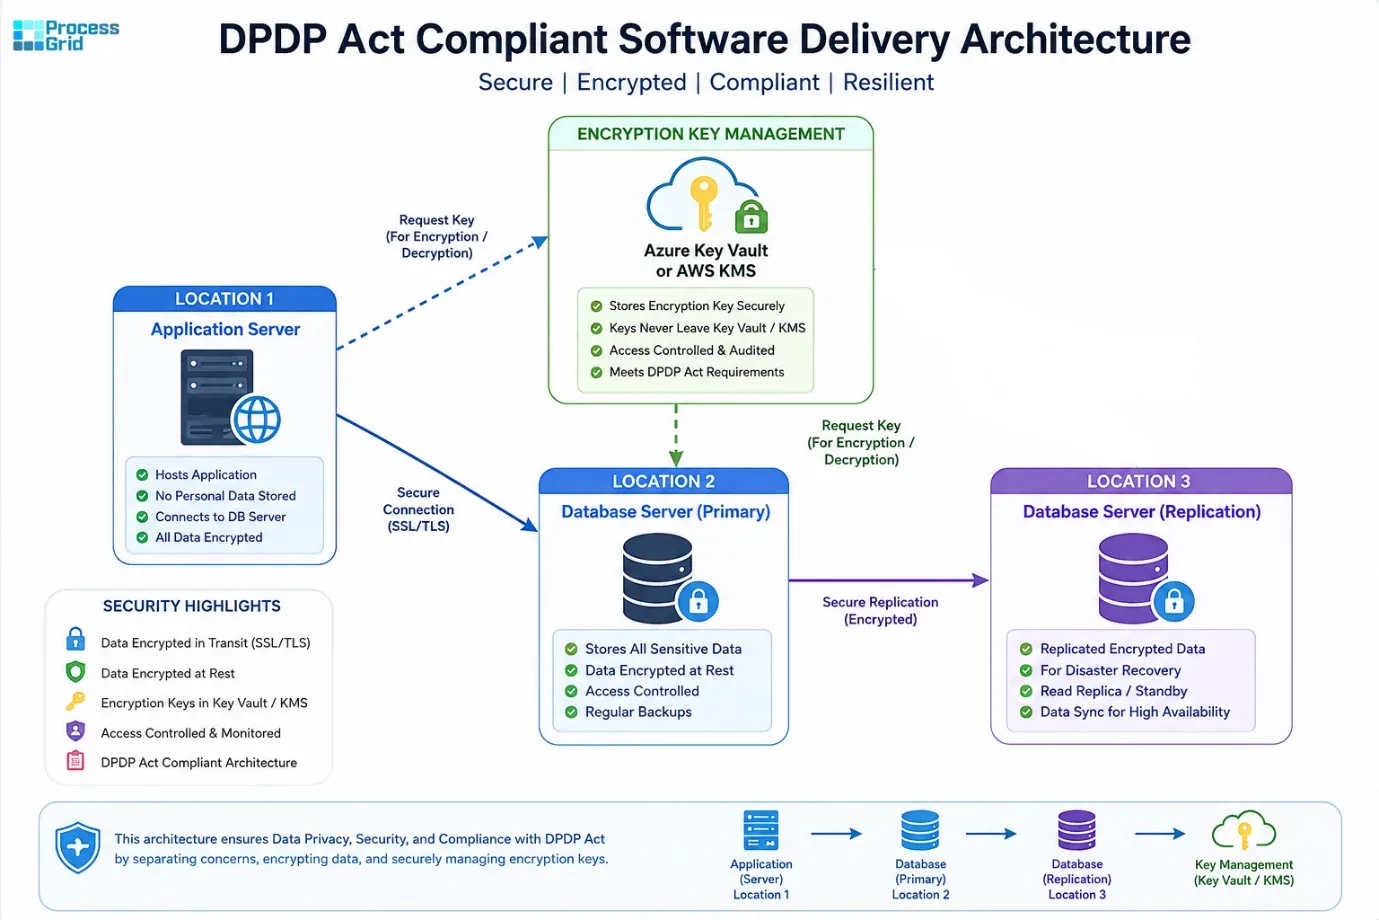
- DPDP Act 2023 gap assessment
- Consent and privacy notice review
- Encryption at rest and in transit
- Access rights and privileged users
- Leakage checks: USB, email, cloud
- Database security and audit trails
- Vendor data-handling review
- Breach response readiness
Our audit process
Clear steps, clear results
Scope & plan›Assess›Test & exploit ethically›Report›Fix & re-test
What you get
A report management can act on
- Executive summary for management
- Findings rated Critical / High / Medium / Low
- Proof of concept for each vulnerability
- Step-by-step remediation guidance
- Re-test after fixes
- Staff awareness training and policy templates
Is your website or data at risk?
Book a scoping call. We’ll agree the scope, timeline and cost before any testing starts.